Context on PHP vulnerabilities
Two critical vulnerabilities in PHP were published on October 21, 2026. These are CVE-2026-109618 and CVE-2026-109619, both rated to CVSS 4.0 score of 9.2. Given that PHP powers roughly 70% of all public websites, the potential attack surface is substantial. Proof-of-concept (PoC) exploit code was rapidly made public. We also observed exploitation attempts against our honeypots shortly after the disclosure. These vulnerabilities, dubbed PHP2Shell, warrant close attention.
Technical details on PHP vulnerabilities
CVE-2026-109618 is an Out-Of-Memory (OOM) vulnerability. It is triggered when processing file uploads submitted with a multipart/form-data Content-Type in an HTTP request. If the memory limit configured in the php.ini file is reached, request processing is interrupted before certain internal structures are properly initialized. As a result, internal data structures are not properly released, leading to memory corruption. This vulnerability can be exploited to achieve Remote Code Execution (RCE).
CVE-2026-109619 is a Use-After-Free (UAF) vulnerability involving certain global variables used for request handling. In specific scenarios, if a request is interrupted, the data referenced by these global variables is freed, but the pointers themselves are not reinitialized. The pointers can therefore still reference memory regions that have been deallocated. Similarly, this flaw can lead to memory corruption and Remote Code Execution (RCE).
Impacted versions by PHP vulnerabilities
The following versions are impacted:
- All versions up to and including 8.2.34
- Version 8.3 up to and including 8.3.35
- Version 8.4 up to and including 8.4.26
- Version 8.5 up to and including 8.5.11
Stormshield Protection Solutions
Stormshield Network Security
An IPS signature was released for Stormshield Network Security (SNS) firewalls on October 23, 2026. It detects and blocks PHP code execution attempts embedded in HTTP multipart/form-data file uploads, targeting the primary exploited code paths observed in the wild. The signature relies on HTTP traffic analysis, which requires TLS decryption (SSL inspection).
This signature is:
- http:mix:374 → Detection of unauthenticated exploitation of PHP (CVE-2026-109618, CVE-2026-109619)
Recommendations
The main recommendation is to update PHP to one of the following versions:
PHP Branch | Patched Version |
8.2 | 8.2.35-1 |
8.3 | 8.3.36-1 |
8.4 | 8.4.27-1 |
8.5 | 8.5.12-1 |
Since no complete mitigation is currently available, compensating controls can be taken to reduce exposure to these vulnerabilities. It is important to note that these settings do not prevent PHP from processing malicious requests. The most effective remediation remains applying the official PHP patches.
- Disable the upload progress feature in the
php.inifile:session.upload_progress.enabled = 0- Note: if your website relies on upload progress bars, they will no longer function.
- Block
multipart/form-datarequests before they reach the PHP service.- This must be configured on a reverse proxy or WAF.
- Ensure this does not break legitimate site functionality before deploying.
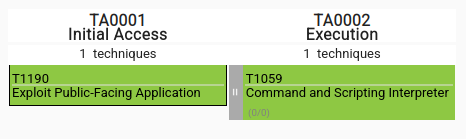
Attack Modeling
MITRE ATT&CK
IOC
Right after the disclosure of the vulnerabilities, our honeypots recorded multiple exploit attempts. This is what we observed:
IOC | Type | Comment |
204.76.203[.]7 | IP | Scanner |
85.11.167[.]243 | IP | Tried to trigger a connection to a C2 to deploy the malware Mirai on the victim's system. |
45.198.224[.]169 | IP | Tried to trigger a connection to a C2 to deploy the malware Mirai on the victim's system. |
92.118.112[.]100 | IP | C2 that hosts the Mirai botnet. Also reported by Sophos. |
217.60.242[.]76 | IP | Tried to trigger a connection a C2 to deploy the crypto stealer RedTail on the victim's system. |
77.90.185[.]20 | IP | Tried to trigger a connection a C2 to deploy the crypto stealer RedTail on the victim's system. |
217.60.102[.]5 | IP | C2 that hosts RedTail |
0c5486f06620e26e316f4b33f318b0d646d5e1133789331aa2fed012360d1486 | Hash | Mirai |
917fcc9131c6e9ca16264a85afc62532297bb39eb9d37765dad536c7c8c7735c | Hash | Dropper RedTail |
f0aa83bbbd2c75e2f71ec16029ee5fcfad59f3a8efa30a500b815f0f6c18d987 | Hash | RedTail |
3f3a11bafabb1a35db913cfe51995f2e357d049e268860175876ae5a93d23892 | Hash | RedTail |
8e1a67a5c03b3cd818f046c7a1605afccc0ee5ce437a0d099881f1872b54bc70 | Hash | RedTail |
d1cac82f44b54b0fd244a9e4122811e9ae108a197c7a65a20fd2e7552683e68e | Hash | RedTail |
d70f917e35813a7ae323e6b2b539d6dbbfc3a3a6599f1fed93430b14ca08b141 | Hash | RedTail |
3f3bf218089d1488617d37f8a5116bb2791eb39ce06a1b5bc9a4cdfe5e94dd39 | Hash | RedTail |