Ensure your remote access is secure with Zero Trust Network Access
Connection
A secure connection for your mobile users
In the age of teleworking, mobility and cloud computing, connections to your applications and resources are made from a variety of locations, many of which are insecure. The Zero Trust Network Access (ZTNA) model is based on a rigorous security architecture and continuous verification of every identity, connection and device, ensuring protected access to your critical data.
Protection
Protection for your critical resources
The rise of BYOD (Bring Your Own Device) and hybrid working is making it harder to manage access to your critical resources. The Zero-Trust model applies strict access control, based on the principle of least privilege, device compliance control and continuous analysis of your employees’ behaviour. By filtering access to your resources, you significantly limit your attack surface and ensure better network security.
Adaptability
Security levels tailored to each business area
Each department within a company or organisation has specific needs for access to business services and applications. The Zero-Trust approach makes it possible to implement an enterprise security policy that is tailored to actual usage, ensuring a fluid user experience while guaranteeing optimum protection. Thanks to network micro-segmentation and dynamic access rules, only legitimate users can interact with the resources they need for their work.
Security
Adopt an advanced ZTNA with Stormshield’s trusted products
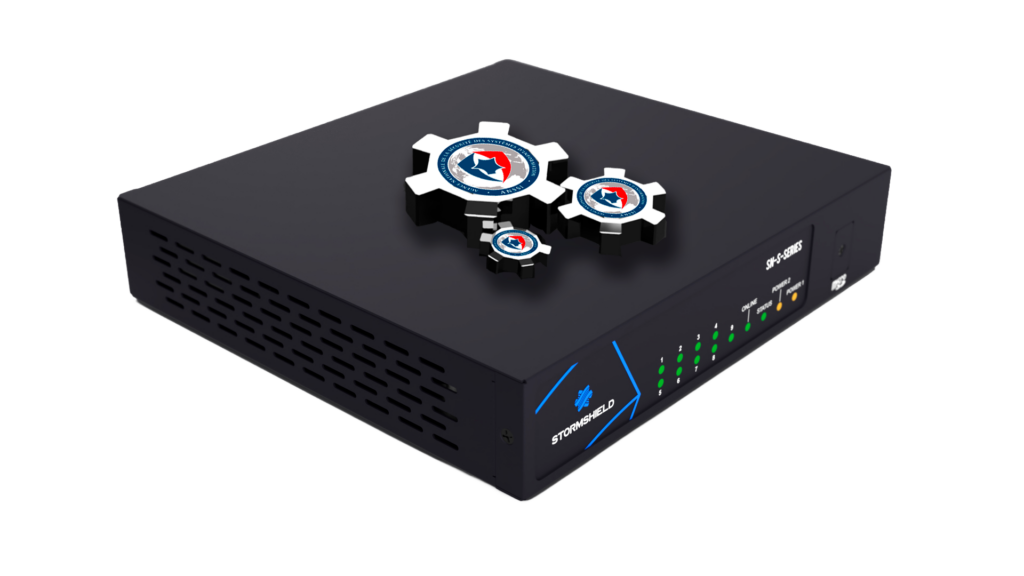
Stormshield Network Security (SNS) cybersecurity products facilitate an advanced Zero-Trust approach, combining robust protection, simplified user-based management of access to your networks and endpoint compliance monitoring. Our next-generation firewalls (NGFWs) natively integrate these features, for seamless deployment of ZTNA at no additional cost. Through its high-level European qualifications and certifications, Stormshield provides trusted, transparent cybersecurity that complies with the most stringent requirements while offering the scalability to tailor your security policy to address changing threats. With products regularly certified and qualified by France’s ANSSI digital security agency, secure your remote accesses with an enhanced ZTNA.
Host Check
Check the compliance of your workstations
SSO & MFA
Enables enhanced authentication for your users
Zero-Trust Policy
Control access to your business applications
Enhanced security
Protect your critical resources
Contact us
“Never trust, always verify.” The Zero Trust and ZTNA philosophies can seem overly simplistic, or indeed complex. Our teams of experts are on hand to help you get a clearer insight, answer any questions you may have about how ZTNA Stormshield works and discuss your plans to migrate to Zero Trust.
F.A.Q
Your questions about ZTNA
What is ZTNA?
The Zero Trust principle turns the cybersecurity approach on its head, through a simple paradigm: no connection is deemed to be secure until employees and their devices have been authenticated, whether the attempted connection comes from within the company or not. The Zero Trust Network Access (ZTNA) philosophy then lets you verify the trustworthiness of your users and their devices, employing technologies such as multi-factor authentication, behavioural analysis and continuous monitoring of endpoint compliance.
How does ZTNA reduce the attack surface?
By applying a policy of least privilege and continuous verification, Zero Trust Network Access drastically limits opportunities for intrusion. Each digital access request is assessed on the basis of several criteria, such as multi-factor authentication (MFA), the security status of the device and the level of risk detected.
How does ZTNA work?
Zero-Trust Network Access is based on a rigorous security architecture in which every attempt to access or connect to the Internet is seen as a potential threat. This means that all users, both internal and external, must be authenticated, approved and authorised before being granted zero-trust network access, regardless of which network they use for logging in. Once authenticated, approved and authorised, employees can access company applications and resources via a trusted gateway.
What is the link between ZTNA and SASE?
ZTNA plays a key role in the SASE (Secure Access Service Edge) model, providing secure access control to cloud applications and applications within the enterprise infrastructure. The combination of these two approaches provides unified cybersecurity. This synergy enables organisations to reduce their dependence on traditional architectures and improve their security approach by guaranteeing a protected and filtered Internet connection.
What are the differences between ZTNA and VPN?
Unlike traditional VPN clients, which grant network access to employees, ZTNA also involves compliance checks on workstations: ZTNA enforces continuous verification and does not permit implicit connections to the corporate network, thereby reducing the attack surface and the risk of compromise. In many cases, the ZTNA gateway therefore offers a more secure alternative to the traditional VPN tunnel. However, some organisations may use a hybrid IT security approach that combines the two solutions, depending on their specific needs.
Is ZTNA suitable for SMEs?
Yes, ZTNA is suitable for SMEs, not just large companies. Stormshield products, for example, are well suited to SMEs: they enable flexible, scalable deployment and simple configuration to deliver secure network access without the need for complex infrastructure.